Blog 3: Centralized AWS Firewall Policy Management with AlgoSec
Overview: Challenges of Hybrid Environments
As enterprises migrate workloads from on-premise to AWS, maintaining consistent security policies becomes a major challenge. AWS Firewall Manager helps centrally manage security rules in the cloud, but organizations often struggle to synchronize these rules with traditional on-premise firewall infrastructure.
A new solution from AlgoSec (available on AWS Marketplace) integrates directly with AWS Firewall Manager, providing unified visibility and management across the entire Hybrid Cloud environment.
1. Introduction to AlgoSec Horizon and ACE
AlgoSec’s solution consists of two integrated main components:
- AlgoSec Horizon: Focuses on visibility, application mapping, and providing business context for network flows.
- AlgoSec Cloud Enterprise (ACE): Manages security policies, risk analysis, and change automation.
Benefits of deploying through AWS Marketplace:
- Simple procurement: Direct integration into AWS billing (Unified billing).
- Fast deployment: Streamlined onboarding for immediate time-to-value.
- Scalability: Easy to extend policy control across all environments.
2. Unified Firewall Policy Visibility
After logging into the ACE console, the AWS Firewall Policies tab displays all deployed AWS firewalls along with their associated policies. Users can view detailed information for each firewall, including VPC, Availability Zones, and Subnets.
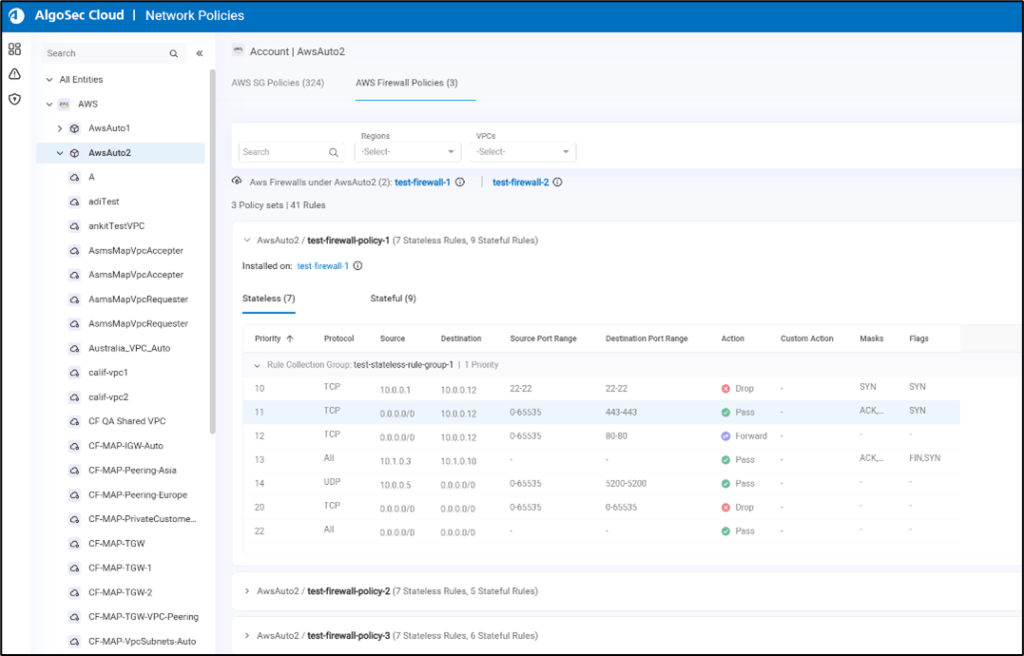
[Figure 1] The main page displays the list of Firewalls, Policy Sets, and Rules.
Contextual visibility is a key strength of the solution. When hovering over a firewall name, the system immediately displays VPC context and related applications.
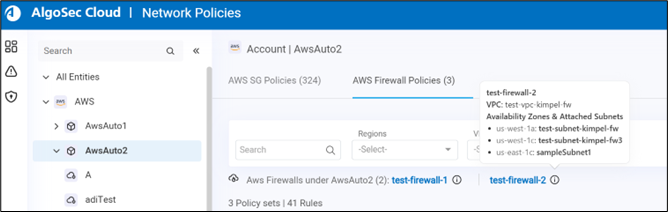
[Figure 2] VPC context displayed when hovering over the Firewall name, helping administrators immediately understand location and scope of impact.
3. Detailed Rule and Application Analysis
AWS Firewall policies typically include two rule groups: Stateless and Stateful. AlgoSec allows you to expand and view details of each rule group.
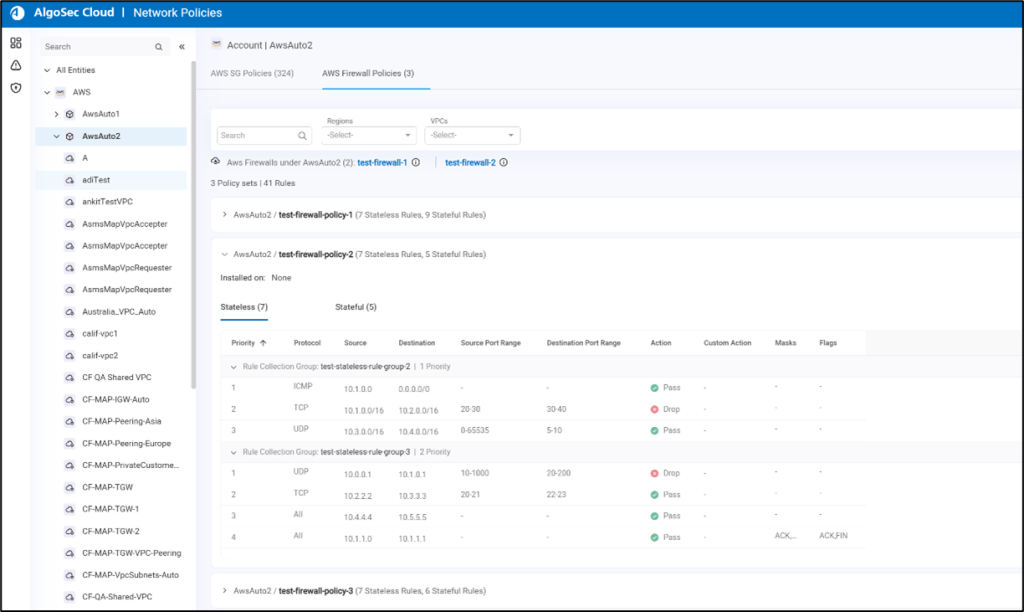
[Figure 3] The expanded view displays detailed Stateless and Stateful rule groups within a policy set.
More importantly, AlgoSec Horizon links this technical information with business context. Users can view Application Diagrams, Application Owners, and connection status from on-premise to cloud.
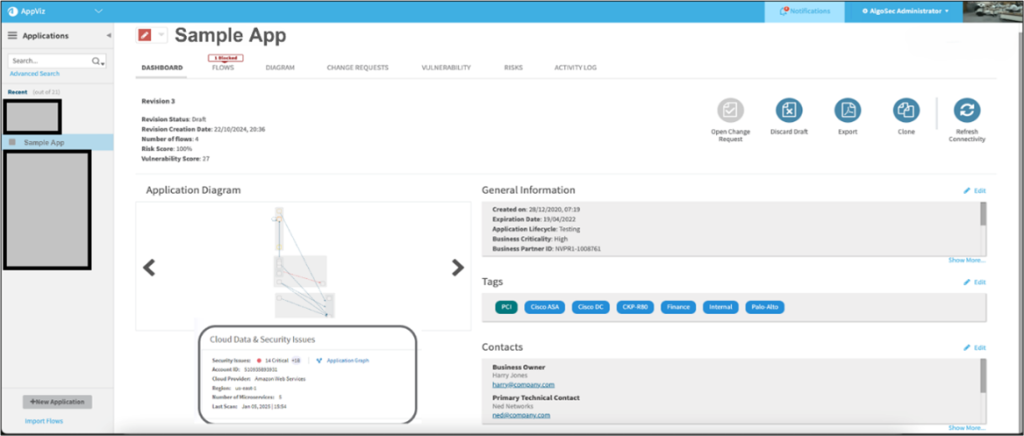
[Figure 4] Application View displays connection diagrams, contact information, and compliance status of business applications.
Conclusion
The combination of AWS Firewall Manager and AlgoSec provides a “single pane of glass” for security teams. Instead of fragmented management, they can now:
- Analyze AWS configurations like traditional firewalls.
- Perform change simulation before applying to avoid business disruption.
- Ensure continuous compliance across the entire Hybrid environment.
Authors
Joseph Hallman
Joseph is a Product Marketing Manager at AlgoSec with over 20 years of experience in networking and data center markets. He has worked at both startups and global enterprises, bringing expertise in sales, product management, and marketing strategy.
Amit Gaur
Amit is a Cloud Infrastructure Architect at AWS, specializing in network architecture design. He helps customers build highly scalable and resilient environments on AWS.
Srivalsan Mannoor Sudhagar
Srivalsan is a Sr. Cloud Infrastructure Architect at Amazon Web Services, Professional Services who brings expertise in Cloud Infrastructure and MLOps platforms.
Saleem Muhammad
Saleem is a Senior Manager of Product Management in AWS Network & Application Protection. He is passionate about building solutions that help customers to secure mission critical workloads.